The St. Luke’s data breach has raised questions about which digital platform was affected and what information may have been exposed. The hospital published a data security incident notice on October 30, 2026. However, the public sources reviewed do not identify the affected platform or its third-party provider by name.
What happened at St. Luke’s?
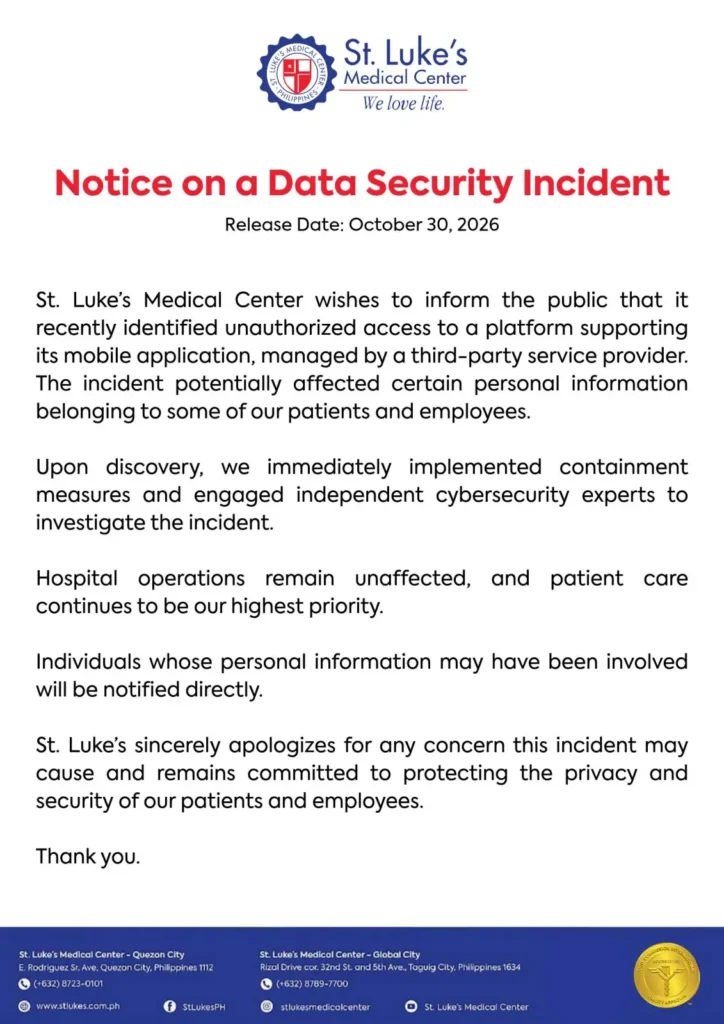
According to the hospital statement reproduced by Daily Tribune on November 2, St. Luke’s identified unauthorized access to a third-party-managed platform supporting its mobile application. Certain personal information belonging to some patients and employees was potentially affected.
The hospital said it introduced containment measures and engaged independent cybersecurity experts to investigate. It also said individuals whose information may have been involved would receive direct notifications, while hospital operations remained unaffected.
What is the affected platform?
The platform’s name has not been established in the public disclosures and reporting reviewed for this article. The description identifies its role in supporting the hospital’s mobile app, but does not identify a particular software product, cloud service, database or vendor.
That distinction matters. Naming an app’s developer or a company that has previously worked with a hospital would not, by itself, establish that the company operated the affected system. Attribution requires a disclosure or investigation finding directly connecting the provider to this incident.
For now, readers should treat any specific platform or vendor name circulating without supporting evidence as unverified.
Has the National Privacy Commission been notified?
ABS-CBN reported on November 2 that St. Luke’s had notified the National Privacy Commission of a personal data breach. Its report was published at 7:22 p.m. Philippine time.
Earlier that day, Daily Tribune’s 4:51 p.m. report said the NPC had yet to comment. These reports reflect different publication times; the earlier absence of a comment should not be treated as evidence that no notification was filed.
Notification is also different from a regulatory finding. The reporting reviewed does not establish that the NPC has determined liability or imposed a penalty.
What is the investigation’s current status?
The hospital has announced the involvement of independent cybersecurity experts. As of this article’s November 3 review, no final technical report or official NPC announcement confirming a separate formal investigation into this incident was located.
The following questions remain unanswered in the sources reviewed:
- How many patients, employees and records were affected?
- Which categories of personal information were involved?
- When did the intrusion happen, and when was it discovered?
- Which provider operated the affected platform?
- Was information copied, published or offered for sale?
- What allowed the unauthorized access?
- Have all affected individuals received notifications?
There is insufficient verified information to describe this as a ransomware attack or to claim that complete medical records were stolen. Those conclusions require evidence beyond the currently available disclosures.
Why a third-party provider does not end the privacy discussion
The NPC’s breach-reporting guidance states that the obligation to notify remains with the personal information controller even when processing is outsourced or subcontracted.
The guidance sets conditions for mandatory reporting, including the nature of the information, suspected unauthorized acquisition and the risk of serious harm. It also provides a 72-hour notification period tied to knowledge of, or reasonable belief in, a reportable breach.
These are general requirements, not findings against St. Luke’s. The public notice’s publication date alone cannot establish whether the hospital complied with a reporting deadline; the relevant discovery and notification details would be needed.
What patients and employees should ask next
A useful individual notification should help the recipient understand what happened to their own information. Questions to raise through the hospital’s official channels include:
- Was my information involved, and which specific details were affected?
- Does the incident require any action on my account?
- Where can I obtain verified updates or report suspicious contact?
- What assistance is available to affected individuals?
The next meaningful update will be one that establishes the scope of the incident, identifies the affected system and explains the investigation’s findings. Until then, specific claims about the provider, stolen records or attacker should be checked against official disclosures.
Sources and reporting note
- St. Luke’s Medical Center: Notice on a Data Security Incident, October 30, 2026
- Daily Tribune: St. Luke’s confirms data breach involving patients, employees, November 2, 2026
- ABS-CBN: St. Luke’s Medical Center notifies NPC of personal data breach, November 2, 2026
- National Privacy Commission: Breach Reporting
Reporting note: The hospital notice is presented as an image. Detailed incident information in this article relies on Daily Tribune’s reproduction of the hospital statement. The accessible ABS-CBN headline confirms its reporting of NPC notification; its article body was not available through text retrieval. This article concerns St. Luke’s Medical Center in the Philippines.